AISecurity Enterprise AI Security Platform
On-Premise AI Security × AI SOC × AI Agent Security × NVIDIA DGX Spark
Turn security alerts into traceable, AI-assisted investigations and controlled response workflows—inside your enterprise environment.
AISecurity is an Enterprise AI Security Platform designed for organizations that need advanced cybersecurity analytics without sending sensitive security data to public AI services.
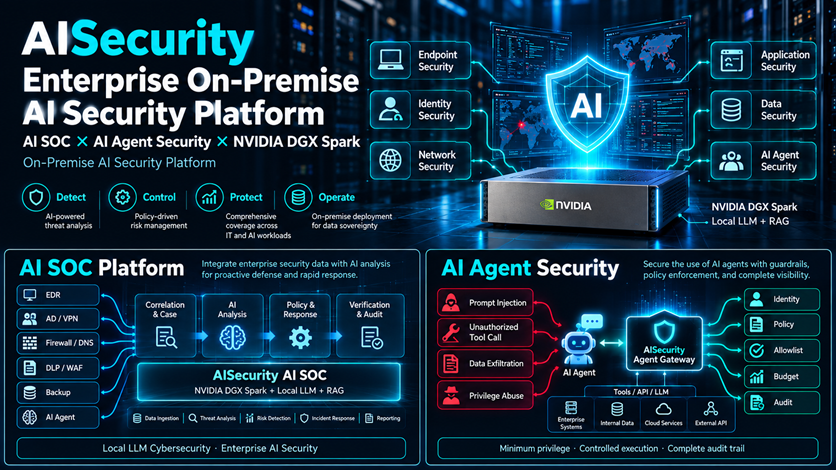
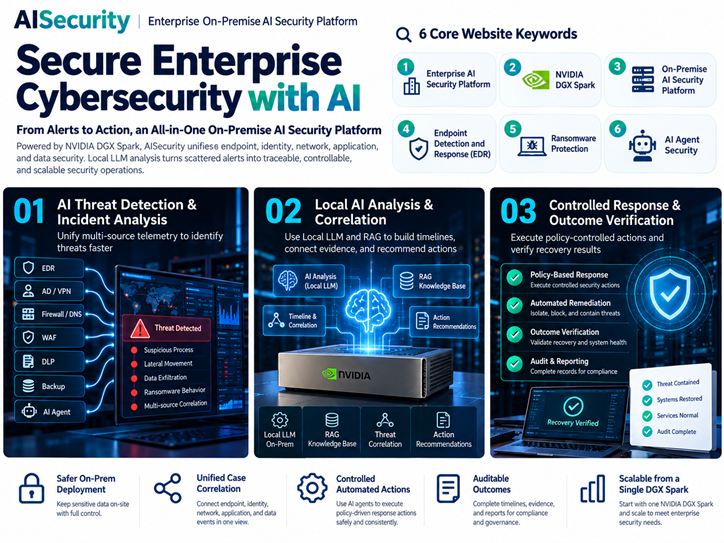
Built around an On-Premise AI Security Platform architecture, AISecurity combines AI SOC, AI Agent Security, Local LLM Security, Enterprise RAG, and NVIDIA DGX Spark to correlate endpoint, identity, network, application, data, and AI-agent events into investigation-ready security cases.
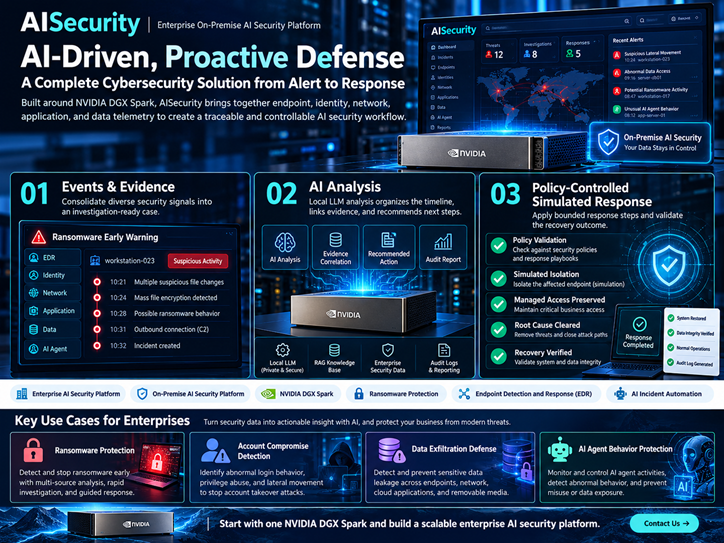
AISecurity creates a security workflow that connects:
Security Events → Evidence Correlation → Local AI Analysis → Policy Control → Controlled Response → Verification → Audit
AI SOC Platform for Enterprise Security Operations
Modern enterprises generate security alerts from multiple independent systems, including:
- EDR
- Active Directory
- VPN
- Firewall
- DNS
- Proxy
- WAF
- DLP
- Backup Systems
- Vulnerability Scanners
- AI Agents
Traditional security operations often require analysts to manually connect these signals.
The AISecurity AI SOC Platform is designed to correlate multi-source security evidence into a unified incident context.
Instead of reviewing disconnected alerts, analysts can investigate:
Who was involved?
Which endpoint was affected?
What happened first?
Which security events are related?
What evidence supports the investigation?
What action should be considered next?
AISecurity helps convert fragmented security telemetry into structured, evidence-driven security cases.
The AI SOC category itself has become an established 2026 enterprise security market; Palo Alto Networks currently describes an AI SOC market focused on governance, scale, response capabilities, and increasingly agentic SOC operating models. Palo Alto Networks
On-Premise AI Security Platform
Cybersecurity logs can contain some of the most sensitive information inside an organization.
AISecurity is designed to support an On-Premise AI Security Platform architecture where security data, investigation records, internal SOPs, RAG knowledge, and Local LLM inference can remain inside the organization’s controlled environment.
Organizations can keep control over:
- Security Logs
- Incident Evidence
- Internal SOPs
- Security Policies
- RAG Knowledge Bases
- Local LLM Inference
- Investigation Records
- AI Agent Activities
This architecture is particularly suitable for organizations requiring:
Private AI
Data Sovereignty
Air-Gapped AI
Restricted Networks
Sensitive Security Operations
NVIDIA has also added enterprise deployment capabilities for DGX Spark, including controlled installation and operation in isolated environments without external internet connectivity. NVIDIA
NVIDIA DGX Spark AI Security Appliance
AISecurity can begin with a single NVIDIA DGX Spark as a compact local AI compute node.
NVIDIA positions DGX Spark as a desktop platform designed to build and run local autonomous agents. It combines the GB10 Grace Blackwell Superchip, 128 GB of unified memory, and the NVIDIA AI software stack for local model and agent workloads. NVIDIA
AISecurity can use NVIDIA DGX Spark for:
- Local LLM Security Analysis
- AI SOC Investigation
- Enterprise RAG
- Security Knowledge Retrieval
- Threat Correlation
- Incident Summarization
- Multilingual Security Analysis
- AI Agent Security
- Policy Recommendation
- Security Reporting
This allows organizations to transform NVIDIA DGX Spark from a general AI development system into the compute foundation for an:
Enterprise AI Security Appliance
NVIDIA now also provides enterprise software support for DGX Spark, including frameworks, models, inference tooling, security, stability, and enterprise support for production-oriented workloads. NVIDIA NGC
AI Agent Security
Secure AI Agents Before They Access Enterprise Tools and Data
AI agents introduce a new security challenge.
Unlike conventional chatbots, enterprise AI agents may be able to:
- Call APIs
- Read enterprise files
- Access databases
- Execute tools
- Connect to cloud services
- Use credentials
- Export information
- Trigger business workflows
AISecurity adds an AI Agent Security layer designed to control how AI agents interact with enterprise systems.
Security controls can address:
- Prompt Injection
- Unauthorized Tool Calls
- Privilege Abuse
- Sensitive Data Exfiltration
- Cross-Case Access
- Unknown Tools
- Abnormal Agent Behavior
- Budget Abuse
- Unauthorized Destinations
The architecture separates AI recommendations from actual execution.
AISecurity Agent Gateway
An AI agent request can pass through:
Trusted Identity
↓
Case / Run Context
↓
Security Policy
↓
Tool Allowlist
↓
Parameter Validation
↓
Budget and Scope Control
↓
Controlled Execution
↓
Audit
This is aligned with the emerging AI Agent Security category. Cisco, for example, describes AI agent security as protecting autonomous AI systems from manipulation and misuse through identity, least privilege, behavioral monitoring, tool governance, and runtime safeguards.
Local LLM Security
AISecurity supports a Local LLM Security architecture where approved AI models can assist cybersecurity analysts without requiring sensitive incident data to be sent to external public models.
Local AI can assist with:
Security Event Summarization
Convert large numbers of security events into concise incident summaries.
Incident Timeline
Organize events chronologically across endpoint, identity, network, and application systems.
Evidence Correlation
Identify relationships among:
User → Device → IP → Application → Event → Data
Security RAG
Retrieve relevant information from:
- Security SOPs
- Response Playbooks
- Internal Policies
- Asset Information
- Previous Security Cases
Investigation Recommendations
Identify missing evidence and recommend the next investigation step.
Multilingual SOC Analysis
Support global security operations where incident records and operational documents may exist in different languages.
AISecurity uses AI to assist analysis and explanation while security policy controls determine what actions may actually be executed.
Enterprise Cybersecurity Use Cases
Ransomware Protection
AISecurity can correlate endpoint processes, file behavior, backup events, recovery mechanism changes, network activity, and other evidence to help identify ransomware precursors and support investigation.
Account Compromise Detection
Combine:
AD + VPN + MFA + Login Events + Endpoint Evidence + Privilege Changes
to identify suspicious account activity and privilege escalation patterns.
Data Exfiltration Defense
Correlate:
Firewall + DNS + Proxy + DLP + File Access + Network Transfer
to identify suspicious outbound activity and investigate potential data exfiltration.
Lateral Movement Investigation
Connect identity, endpoint, remote management, network, and application evidence to identify suspicious movement across enterprise systems.
Vulnerability and Supply Chain Security
Incorporate:
- Vulnerability Data
- Software Versions
- SBOM
- Container Images
- CI/CD Events
- Asset Criticality
to improve remediation prioritization.
AI Agent Behavior Protection
Monitor AI agent behavior and enforce policies around:
- Identity
- Tools
- APIs
- Data Access
- Export
- Execution Scope
- Audit
AISecurity vs. Traditional Security Operations
Traditional security environments often produce disconnected alerts.
AISecurity adds an AI-driven investigation and control layer:
Traditional Alert
→
Evidence Correlation
→
AI SOC Investigation
→
Local LLM Analysis
→
Policy-Controlled Response
→
Verification
→
Audit
AISecurity is designed to integrate with existing enterprise security infrastructure rather than requiring organizations to replace every EDR, firewall, IAM, DLP, or security tool.
Built for Security-Sensitive Organizations
AISecurity is designed for:
- Enterprises
- Manufacturing
- Government
- Financial Services
- Healthcare
- Technology Companies
- Security Operations Centers
- Critical Infrastructure
- Private AI Environments
- Air-Gapped Networks
- AI Agent Deployments
Build Your Private AI Security Center
Start with one NVIDIA DGX Spark and integrate existing:
EDR + AD + VPN + Firewall + DNS + DLP + WAF + Backup + AI Agents
to establish an enterprise AI security workflow:
Detect → Correlate → Analyze → Control → Respond → Verify → Audit
AISecurity — Enterprise On-Premise AI Security Platform